Does Your Medical Practice Need Cyber Insurance?
Medical practices store some of the most sensitive information businesses can possess.
Patient names.
Dates of birth.
Insurance information.
Medical histories.
Payment information.
Prescription information.
Electronic health records.
That makes healthcare organizations attractive targets for cybercriminals.
Yet many small and midsize medical practices still assume that their general liability or medical malpractice policy will automatically pay for a major cyber incident.
That assumption can be dangerous.
Cyber liability insurance is designed to address risks that traditional business and malpractice insurance may not adequately cover.
Imagine This Happens Monday Morning
An employee receives an email appearing to come from Microsoft.
The message says the employee’s password is about to expire.
They click the link and sign in.
Nothing appears to happen.
Several days later, someone begins accessing the practice’s email accounts.
Patient information is exposed.
Fraudulent payment instructions are sent.
Systems become unavailable.
Now the practice has several problems simultaneously.
It may need cybersecurity specialists.
Legal counsel.
Patient notification.
Credit monitoring.
Data restoration.
Public relations support.
And potentially assistance responding to regulatory obligations.
This is exactly why cyber risk should be treated as a business exposure rather than simply an IT problem.
Medical Malpractice Insurance and Cyber Insurance Solve Different Problems
Medical malpractice coverage generally focuses on allegations arising from professional healthcare services.
Cyber insurance focuses on digital and privacy-related exposures.
There may occasionally be overlap depending on the circumstances and policy language, but physicians should not assume professional liability coverage provides comprehensive protection after a cyberattack.
A medical practice needs to understand which policy is expected to respond to each type of loss.
What Can Cyber Insurance Cover?
Coverage differs substantially among insurers, but a cyber policy may include protection for expenses associated with events such as:
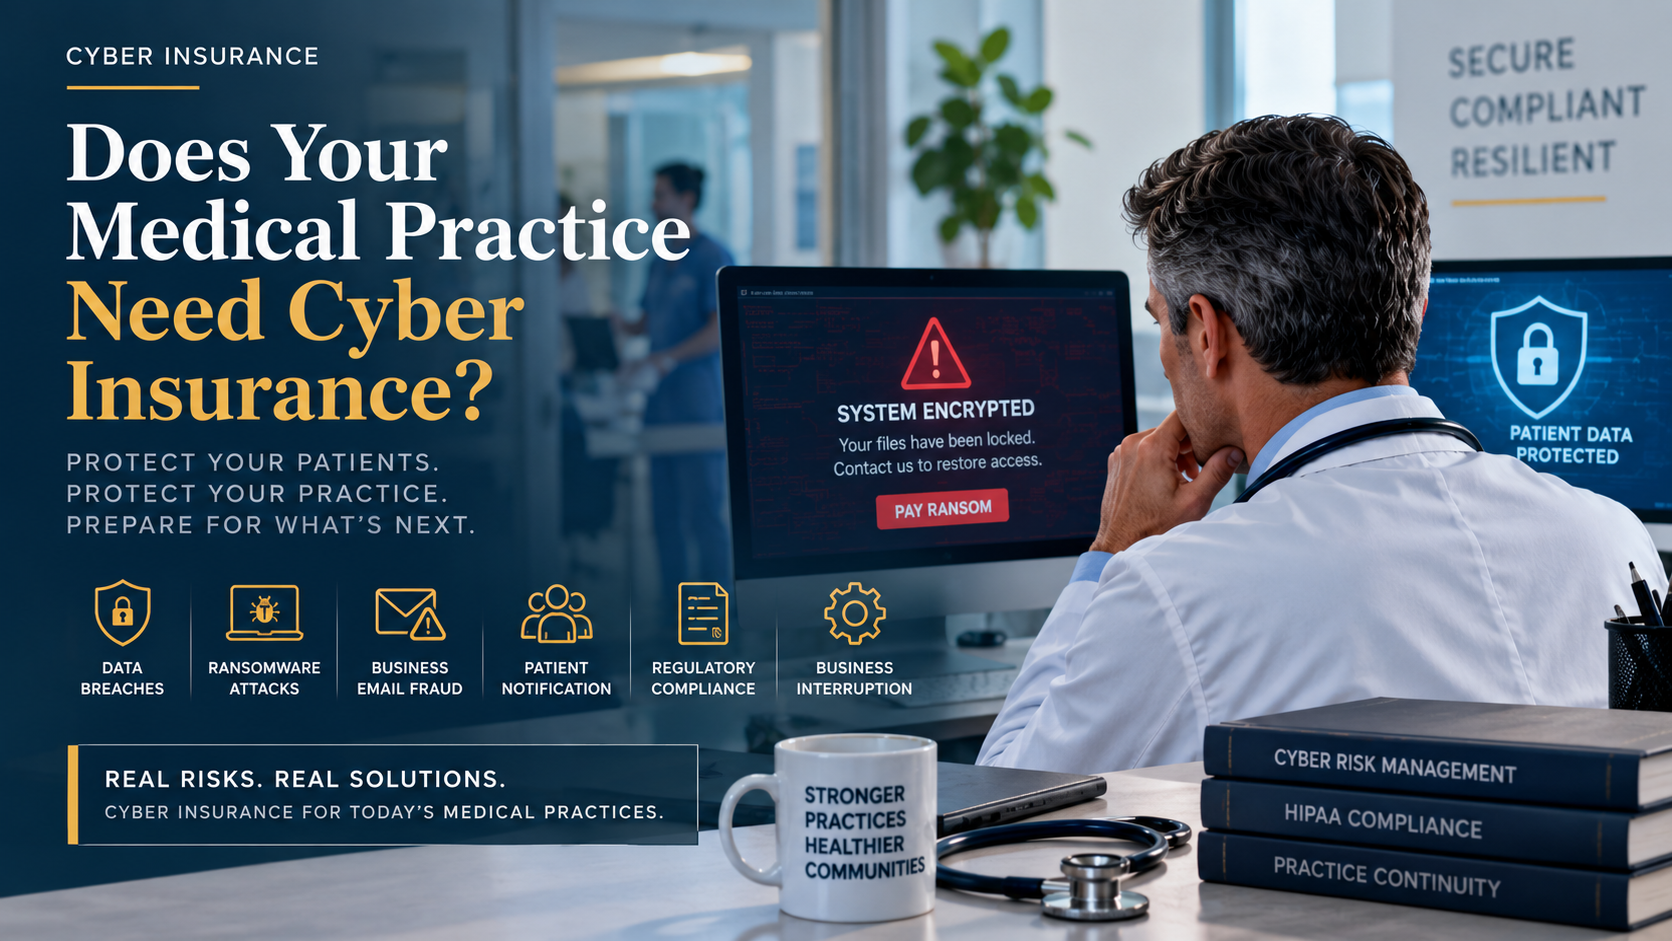
Data breaches, ransomware attacks, network interruption, forensic investigations, privacy incidents, notification expenses, restoration costs and certain third-party liability claims.
Some policies may also provide access to specialized breach-response professionals.
That service can be extremely valuable.
After a cyber incident, figuring out who to call can waste critical time.
A strong cyber insurance policy may help coordinate the response.
Ransomware Is Not the Only Threat
Ransomware receives a great deal of attention, but medical practices face several other cyber exposures.
Business email compromise is one.
An attacker may gain access to an employee’s email account and impersonate staff.
Phishing is another.
Employees may unknowingly provide credentials to a fraudulent website.
Lost laptops, stolen devices, improperly configured cloud storage and unauthorized access can also create privacy problems.
And not every incident requires a sophisticated hacker.
Human error continues to create significant exposure.
Small Practices Are Not Too Small to Attack
Some medical practices believe cybercriminals only target hospitals and massive health systems.
That is a dangerous assumption.
Smaller practices can actually be attractive because attackers may expect weaker security controls.
A physician office may not have a full cybersecurity department.
Employees may reuse passwords.
Multifactor authentication may not be enabled everywhere.
Backups may not be tested regularly.
Software updates may be delayed.
An attacker does not need to care how large the organization is.
They only need to find an opening.
HIPAA Adds Another Layer of Complexity
Medical practices also operate within a healthcare privacy environment.
A cybersecurity incident involving protected health information can create obligations that do not exist for many ordinary businesses.
That may include determining what information was affected, who was affected and what notifications are required.
This is why cybersecurity should involve more than purchasing software.
Practices should evaluate technical controls, employee procedures, vendor relationships and insurance together.
Your Vendors Can Create Cyber Exposure Too
Medical practices rely on outside vendors for:
Billing, cloud applications, electronic health records, patient scheduling, payment processing, telemedicine, laboratories and other services.
Even when your own systems are secure, a third-party vendor may experience an incident.
Practices should understand how vendor-related events are handled under their cyber coverage.
Do not assume every third-party breach automatically triggers coverage.
Policy wording matters.
Business Interruption Can Become Expensive Quickly
Consider what happens if your scheduling platform or EHR becomes unavailable.
Can the practice continue treating patients?
Can staff access charts?
Can appointments be confirmed?
Can billing continue?
Even several days of disruption can create significant operational problems.
Cyber coverage may include business interruption protection under certain circumstances, but definitions, waiting periods and coverage triggers vary.
These provisions deserve careful review.
Cyber Insurance Applications Are Becoming More Detailed
Insurers increasingly want to understand an organization’s cybersecurity controls.
Medical practices may be asked about:
Multifactor authentication.
Backups.
Endpoint protection.
Employee security training.
Email security.
Access controls.
Incident response planning.
Remote access.
Vendor management.
These are not meaningless boxes on an application.
Strong controls can affect eligibility, pricing and available terms.
Practices should therefore begin reviewing cybersecurity before they need insurance rather than discovering weaknesses during underwriting.
Cyber Coverage Should Be Part of a Broader Practice Risk Review
Medical practices face multiple interconnected risks.
Professional liability protects against one category.
Cyber insurance addresses another.
Business property, general liability, employment practices, workers’ compensation and other policies may address additional exposures depending on the practice.
Insurance works best when the entire organization is considered rather than purchasing individual policies in isolation.
Island Insurance Group provides several free tools designed to help business owners evaluate risk.
Visit our Insurance Tools & Resources Center to explore available assessments.
Medical practice owners can also complete the free Small Business Insurance Assessment Tool.
Review Your Medical Practice’s Cyber Exposure
Cyber insurance does not prevent an attack.
Its purpose is to help transfer portions of the financial risk associated with certain covered cyber events.
The right policy depends on the practice’s size, patient information, technology, revenue, security controls, vendors and other factors.
Island Insurance Group helps medical practices evaluate cyber and business insurance options alongside professional liability coverage.
Samuel Bennett — Licensed Insurance Agent
Island Insurance Group
sam@islandinsurancegroup.com
954-804-8144
Schedule a 30-Minute Insurance Review
Physicians who also want to evaluate malpractice underwriting factors can use our free Physician Underwriting Assessment.
Coverage varies substantially by insurer. Cyber insurance may contain exclusions, sublimits, waiting periods and specific security requirements. This article is for general informational purposes only.